Convoys · Compliance and Assurance
The Compliance and Assurance Convoy.
Maps regulators' technical controls onto your Kubernetes cluster, enforces the controls the cluster can enforce, checks the ones it can only observe, and writes dated evidence for each regime every day: a report your team can act on, and a record your assessor can read, in each regulator's own numbering. A glossary at the end of the page explains each regulator and standard it names.
The convoy's regimes are NCA ECC, SAMA CSF, QCB, Qatar NIA, UAE IA, CBUAE, MAS TRM and CBI. The regimes coming soon are listed under Regimes. The screenshots on this page are taken on a test cluster with sample workloads.
The Compliance and Assurance Convoy and Mamluk LLC-FZ are not affiliated with or endorsed by any regulatory authority whose regime the convoy covers.
The problem
Evidence that is out of date the day after it is gathered.
A regulated organisation answers to its regulator for every system it runs, and a Kubernetes platform is a moving one: workloads are deployed, scaled and replaced many times a day. The evidence an assessment asks for, such as which images run, whether they carry known vulnerabilities, who may do what, whether workloads are separated and whether logs are kept, is usually gathered by hand before each assessment, in screenshots and spreadsheets that describe the cluster as it was on one day.
Between assessments that evidence goes out of date, and a control that drifted is found at the next assessment rather than when it drifted. Each regulator also asks in its own terms, so an organisation that answers to two regulators gathers much of the same evidence twice.
The convoy makes the cluster produce its own evidence, every day, against the regime's own control numbers, and keeps it where your organisation keeps its data.
How it works
Four sources of evidence, one report per regime.
The convoy installs into your cluster beside the Tersane charts for Kyverno and trivy-operator. Kyverno is an open-source policy engine for Kubernetes. The convoy uses it for what Kubernetes cannot do by itself, such as verifying an image's signature, and reads the results of its own policies from Kyverno's policy reports. trivy-operator is an open-source security scanner that runs inside the cluster. It scans every workload's images for known vulnerabilities, and audits each workload's configuration and the permissions granted in the cluster.
The convoy reads four sources, joins them to the regime's controls through a single mapping, and writes the evidence to a volume in its own namespace. A namespace is a named partition of a Kubernetes cluster, which usually holds one application's or one team's workloads. Permissions and policies are commonly set per namespace.
Admission policies, in two layers
An admission policy is a rule Kubernetes applies to each object as it is created or changed, before the object is stored. It can warn about the object and record the result, or refuse the object.
Every control the Kubernetes API server can decide by itself ships as a built-in
ValidatingAdmissionPolicy: images only from your registries, no service
account token mounted by default, resource limits set, environment and data
classification labels on every namespace, and similar. This layer needs no policy engine,
so it holds if Kyverno is removed. Kyverno adds only what the API server cannot do: image
signature verification, a generated default-deny NetworkPolicy
per namespace (off by default), and policy reports for the built-in layer.
A NetworkPolicy is the Kubernetes object that states which network traffic may reach a group of workloads. A workload that no NetworkPolicy selects accepts traffic from anywhere in the cluster.
You name your authorised registries, in registries.allowed; the convoy warns
about, or once you choose refuses, an image from any other registry, and the report evidences
the result for every workload.
A newly installed convoy refuses nothing. Every policy warns and records until you set that control to deny, after the report has shown what it would refuse.
The cluster's own scanners
trivy-operator scans every workload's images for known vulnerabilities against a database refreshed every six hours, and audits each workload's configuration and every role's permissions. The convoy computes each result itself from trivy-operator's raw reports, so a check that has not yet run is reported as not evaluated, never as passed.
One of trivy-operator's checks is not used. Its list of trusted registries names only the registries of three cloud providers, so it reports every registry in your own data centre, and every in-country registry other than theirs, as untrusted. The convoy judges where images come from against the registries you name instead.
Platform and node facts
On the Bahriya Kubernetes Engine, the platform declares the controls it provides, such as audit logging, encryption of Secrets and a trusted time source, and the convoy reports each one, switched on or off, as provided by the platform. A short read-only Job on each node records the time source, the kubelet's configuration in effect and the permissions of named files. The convoy reads the cluster's configuration; it never changes it.
The evidence collector
Once a day, one run per regime joins every result to the regime's requirements and writes the report in HTML and PDF, assessment results in Open Security Controls Assessment Language (OSCAL), and a manifest of SHA-256 digests, signed with your key when you provide one. The files stay on a volume in the convoy's namespace, served read-only inside the cluster. OSCAL is NIST's machine-readable format for control catalogues and assessment results. Governance, risk and compliance tools import results in it, so findings need not be typed in again.
A worked example
How regulators' requirements become one set of evidence.
A regulator writes its requirements in its own words and numbering. A cluster can show only facts: which image a container runs, what that image contains, who holds which permission. The convoy joins the two through a reference catalogue, NIST Special Publication 800-53, Revision 5 (SP 800-53), published by the National Institute of Standards and Technology (NIST). NIST is the United States government's standards agency. Its security publications are free to use, and regulators and auditors outside the United States also use them as a common reference. SP 800-53 is a control catalogue: a numbered list of safeguards, each stating one thing an organisation should do, such as AC-6, least privilege, or AU-11, keeping audit records for a set period. Its controls are grouped in 20 families, and because the catalogue is detailed and open, it serves as a common language between regulations that are each written in their own terms.
The join takes three steps. Each requirement is mapped to the NIST controls that state the same safeguard; each of those controls is mapped to the checks that evidence it in a cluster; and each check examines the cluster's objects. The example below follows one safeguard, finding and fixing known vulnerabilities, from a requirement in each regime below to the same evidence.
-
1. The regulators' requirements
Each of these regimes asks, in its own words, that known vulnerabilities are found and dealt with. In Mamluk's paraphrase:
- National Cybersecurity Authority (NCA), ECC 2-10-3-1: vulnerabilities assessed and detected periodically.
- Qatar Central Bank (QCB), 9.4.3.1: automated and manual vulnerability assessment at least twice a year, each compared with the last to confirm remediation.
- UAE Information Assurance Standard (UAE IA), T3.3.2: vulnerabilities in new systems found and planned for before production, production systems tested, and vulnerabilities addressed.
- National Information Assurance Standard (Qatar NIA), SS 14: vulnerabilities in standard environments reduced, with patching kept current among other hardening measures.
- SAMA Cyber Security Framework (SAMA CSF), 3.3.17.3.b: scans as often as risk requires.
- Central Bank of the UAE (CBUAE), Operational Risk Management Regulation, 8.7.3: actionable intelligence used to keep aware of vulnerabilities in applications, networks and ICT systems.
- Monetary Authority of Singapore (MAS), Notice FSM-N06, 4.2(a): security patches applied to every system within a time set by the risk each vulnerability poses; the notice is binding.
NCA is Saudi Arabia's national authority for cybersecurity. It sets the cybersecurity requirements for government entities and the operators of critical national infrastructure, and assesses compliance with them. QCB is Qatar's central bank and the regulator of its banks. Its circular on technology risks, issued in January 2018, sets the technology and cybersecurity requirements for the banks it regulates, in 516 numbered statements. The Information Assurance Standard is the UAE's federal standard of security controls, binding on federal government entities and on critical information infrastructure, banks among them. Version 2.1 holds 134 controls in fifteen families, and maps each control to NIST SP 800-53 itself. The National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency in May 2023, applies to all organisations, which it defines as businesses operating within the State of Qatar, and to their information assets. It holds 356 control statements in 26 domains, and marks each as a baseline or an additional control. The Cyber Security Framework sets the cybersecurity requirements for the organisations SAMA regulates, as control considerations in four domains. It is distinct from NIST's Cybersecurity Framework, which is also abbreviated CSF. The CBUAE licenses and regulates banks and other financial institutions in the United Arab Emirates. Its Operational Risk Management Regulation sets their requirements for information and communications technology and cybersecurity, and requires them to comply with the cybersecurity regulations of the other UAE authorities. The Monetary Authority of Singapore is Singapore's central bank and the regulator of its financial sector. It issues binding notices to banks, insurers and capital markets intermediaries, and guidelines that set out the good practice it expects them to adopt.
The convoy classes each as checked, with partial coverage: the cluster can show that its images are scanned and what the scans found, while the parts a cluster cannot show, such as manual assessment, the comparison between assessments or the removal of file shares, are the organisation's to evidence, and the report asks for that evidence.
-
2. The NIST controls they map to
NIST SP 800-53 states the safeguard in two controls. RA-5, vulnerability monitoring and scanning, asks that systems are scanned for vulnerabilities and the results analysed. SI-2, flaw remediation, asks that flaws are identified and corrected. Every requirement shown is mapped to RA-5 except Qatar's, which concerns patching and is mapped to SI-2; the UAE's requirement, which covers both finding and addressing, and Singapore's, which asks for patches within a time set by risk, are mapped to SI-2 as well.
-
3. The checks behind those controls
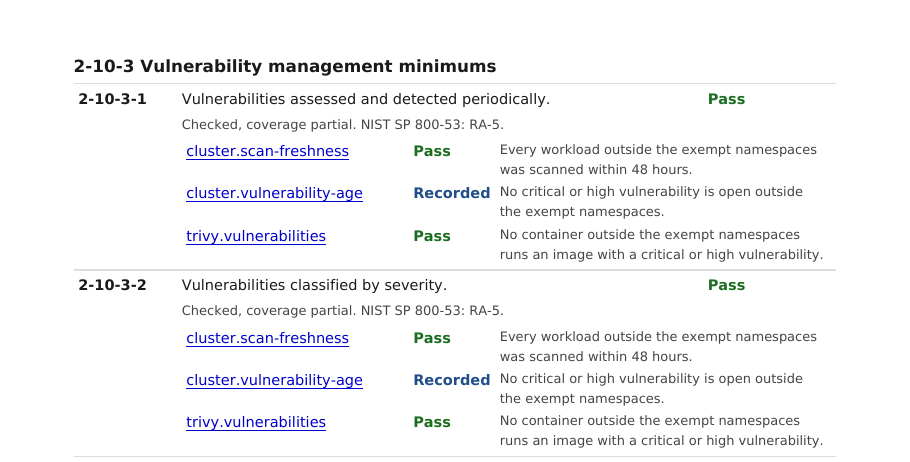
trivy-operator scans the images of every workload in the cluster, against a vulnerability database refreshed every six hours, and records what it finds. The check trivy.vulnerabilities reads those scans: it fails when any container, outside the namespaces of Kubernetes itself, the platform and the convoy, runs an image with a critical or high vulnerability. Beside it, cluster.scan-freshness fails when a workload has not been scanned within 48 hours, so an old scan cannot stand in for a current one, and cluster.vulnerability-age records how long each open critical or high vulnerability has been reported.
-
4. What the report shows
A requirement passes only when every check behind it passes. A cluster in which one container runs an outdated image with a critical vulnerability therefore fails every one of these requirements, and each report names the container, the vulnerability, the version that fixes it and how long it has been open. Once the image is rebuilt and scanned again, the same requirements pass, provided their other checks pass too.
-
5. One cluster, every regulator
When an organisation selects more than one regime, such as a bank in Saudi Arabia that answers to both NCA ECC and SAMA CSF, the convoy reads the same scans once, and the same findings appear under each regime's own requirement, in its regulator's numbering.
That is why the mapping runs through NIST. Each regulator's requirements are mapped to NIST once; the checks are mapped to NIST once; and a cluster's evidence then serves every regulator whose requirements reach the same controls. A new regime adds its requirements and their NIST mapping, and reuses every check.
What you receive
Every requirement, with exactly one result.
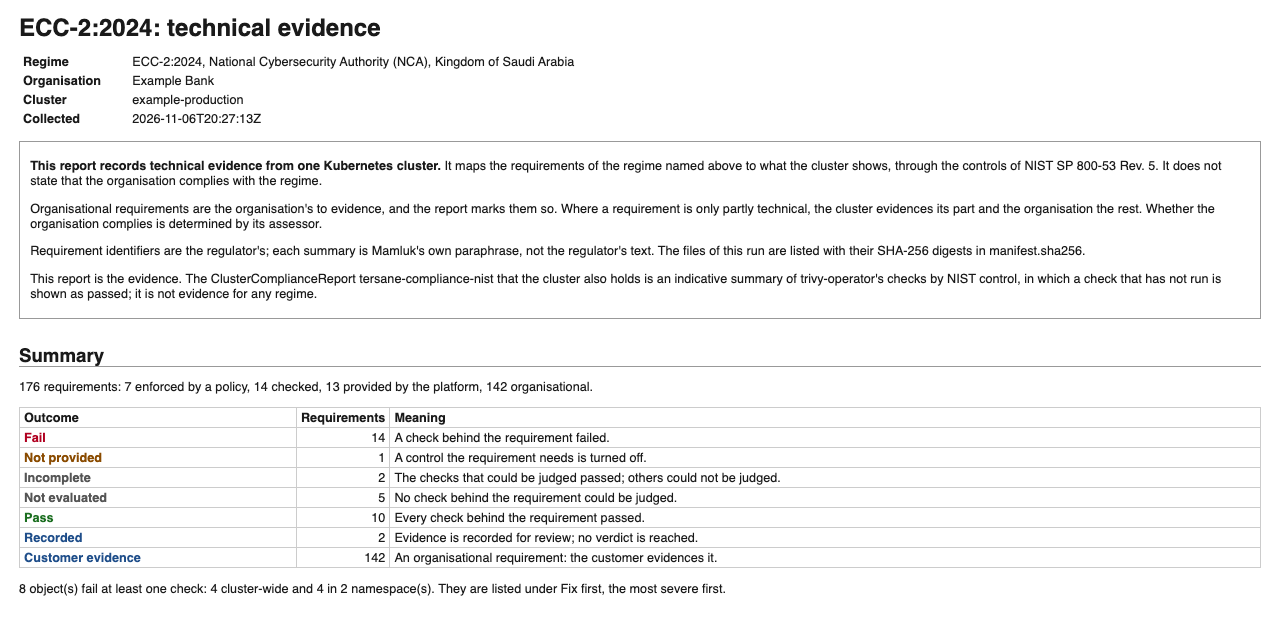
Each run's report lists every requirement of the regime, in the regulator's own numbering, with one result: pass, fail, incomplete where some checks could not yet be judged, recorded where the evidence is kept for review without a verdict, or customer evidence for an organisational requirement. Every technical result names the checks that produced it. The report states on its first page that it records technical evidence and that compliance is determined by your assessor.
Each image opens at full size when selected.
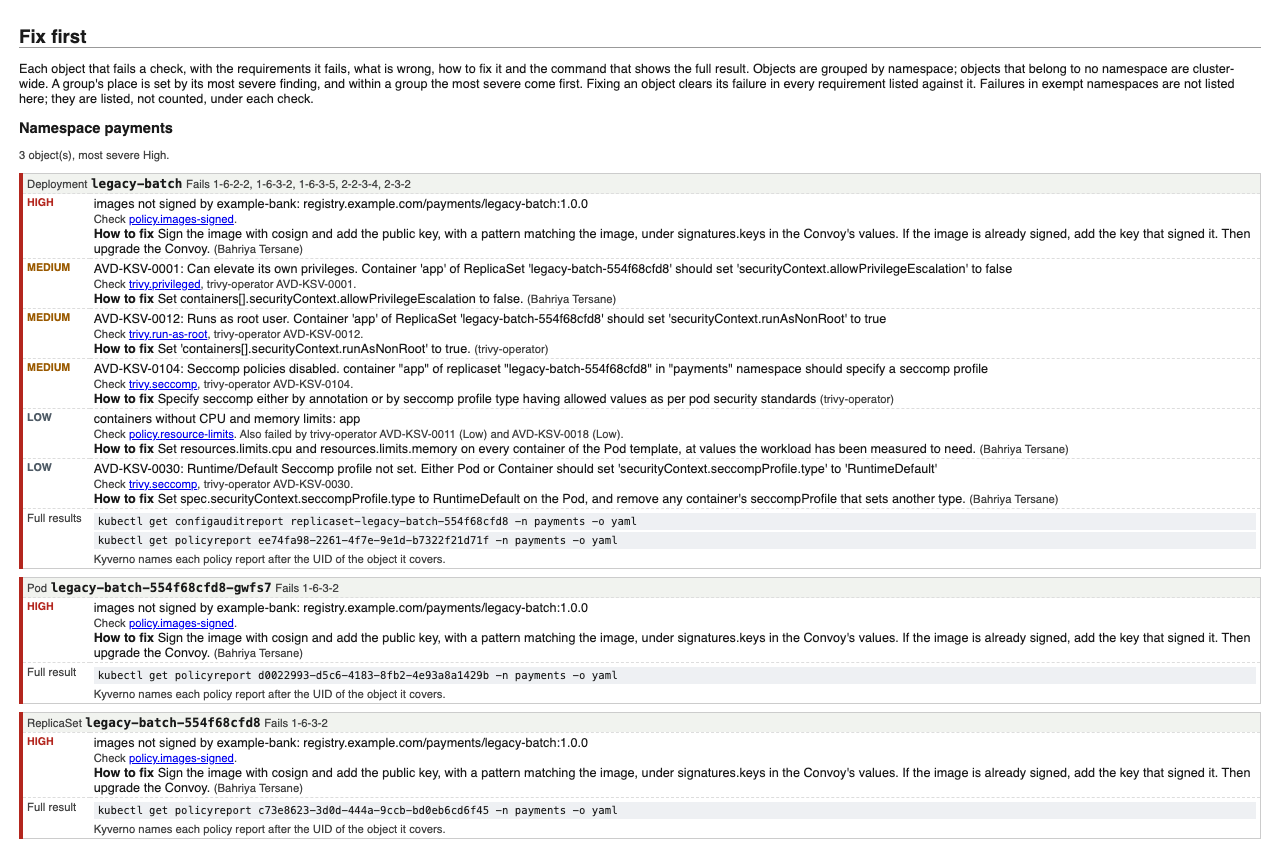
What to fix first
Before the requirements, the report lists every object that fails a check, grouped by namespace and ordered by the most severe finding: the workload, what is wrong with it, the requirements it affects, and the change that fixes it. The team that owns a namespace reads its own section and starts at the top.
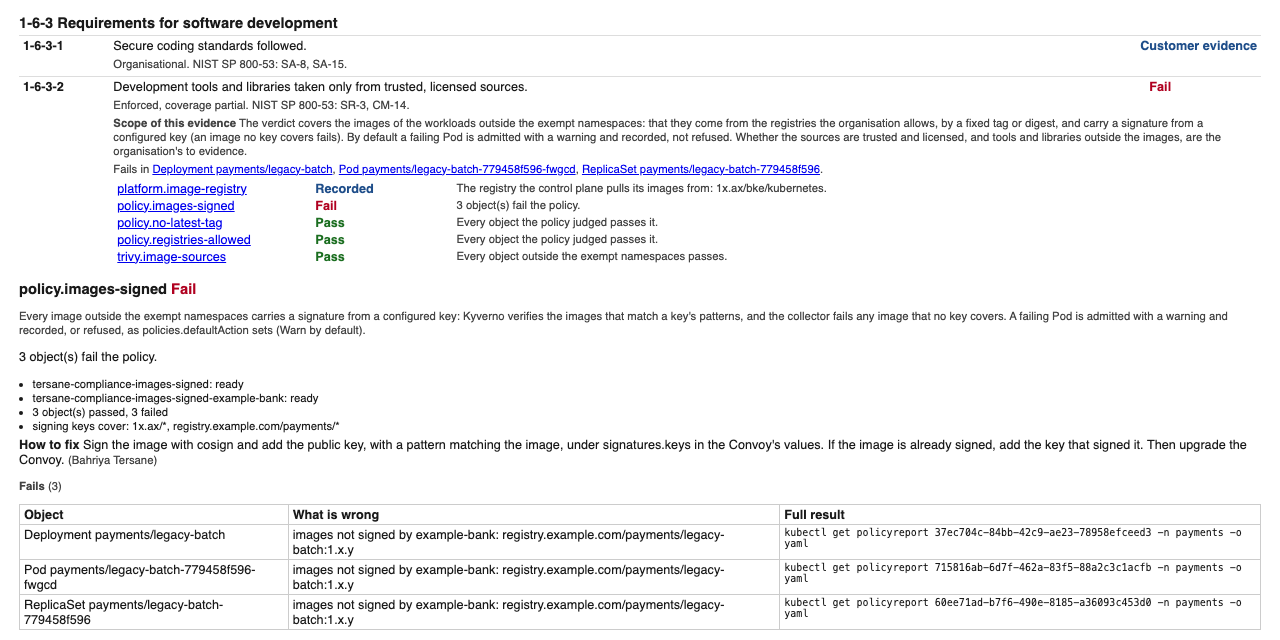
Each requirement, with its evidence
Each requirement shows its result, the NIST controls it maps to, and each check behind it: what the check establishes, what it found, and the objects that pass, fail or are exempt. An assessor can follow any result back to the cluster object that produced it.
The same report as PDF, and OSCAL for your tools
The PDF is rendered from the same report inside the cluster, with no browser and nothing fetched, and carries the same requirements and results. The OSCAL 1.1 assessment results give one finding per requirement, in a form governance, risk and compliance tools can import; every release's output is validated against the OSCAL schema.
Every file is listed with its SHA-256 digest in a manifest, so a copy given to an assessor can be checked against the original.
Sample report
- Sample report, NCA ECC (PDF)
- Sample report, SAMA CSF (PDF)
- Sample report, QCB (PDF)
- Sample report, Qatar NIA (PDF)
- Sample report, UAE IA (PDF)
- Sample report, CBUAE (PDF)
- Sample report, MAS TRM (PDF)
- Sample report, CBI (PDF)
A sample, written by the convoy on a test cluster with sample workloads, for the organisation "Example Bank". Its image versions and cluster name are placeholders, and its run date and regime version are those of the sample, not of a release.
{
  "uuid": "556148ca-7fe8-5dab-8a6a-e38772270d7a",
  "title": "ECC-2:2024 2-10-3-1",
  "description": "Vulnerabilities assessed and detected periodically.",
  "props": [
    {
      "name": "outcome",
      "ns": "https://tersane.bahriya.cloud/ns/oscal",
      "value": "pass"
    },
    {
      "name": "class",
      "ns": "https://tersane.bahriya.cloud/ns/oscal",
      "value": "checked"
    },
    {
      "name": "nist-sp800-53r5",
      "ns": "https://tersane.bahriya.cloud/ns/oscal",
      "value": "RA-5"
    }
  ],
  "target": {
    "type": "objective-id",
    "target-id": "nca-ecc_2-10-3-1",
    "status": { "state": "satisfied" }
  },
  "related-observations": [
    { "observation-uuid": "1fa79b01-9fe2-5f24-8a53-aeea91bed4a1" },
    { "observation-uuid": "b1d44243-7f5f-59ad-a4b2-18e010cce487" },
    { "observation-uuid": "0740bc82-2421-538c-81c3-80fd697352b6" }
  ]
}Available regimes
Each regime in its regulator's own numbering.
Each regime lists every requirement of its regulator, under the regulator's own identifiers, with a short description written by Mamluk; no regulator's text is reproduced. Each requirement is classed by how it is evidenced: enforced by a policy, checked in the cluster, provided by the platform, or organisational, which the organisation evidences and the report marks as such. An organisation licenses the regimes it answers to, and the convoy reports each of them from the same cluster.
Saudi Arabia
NCA Essential Cybersecurity Controls, ECC-2:2024
National Cybersecurity Authority (NCA)
Qatar
National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency
National Cyber Security Agency (NCSA)
United Arab Emirates
UAE Information Assurance Standard v2.1
UAE Cyber Security Council
United Arab Emirates
Central Bank of the UAE, Operational Risk Management Regulation, for banks
Central Bank of the UAE (CBUAE)
Singapore
Monetary Authority of Singapore, Technology Risk Management
Monetary Authority of Singapore (MAS)
Iraq
Central Bank of Iraq, Cyber Resilience Controls and Banking Reform Standards B2, B3, B7 and B9
Central Bank of Iraq (CBI)
One mapping for every regime
Keyed to NIST, so one cluster's evidence serves each regulator.
Every check the convoy runs is mapped once, to the NIST SP 800-53 Rev. 5 controls it evidences. Each regime's requirements are mapped to the same NIST controls. A requirement's result is therefore drawn from the checks of the NIST controls it maps to, and a new regime is added as data, its requirements and their NIST mapping, without a new policy, scanner or chart.
For an organisation that answers to more than one regulator, such as a bank in Qatar that must meet both the QCB's circular and Qatar NIA, the convoy collects evidence for each regime every day from the same cluster and the same scanner and policy reports, and reports each regime in its own numbering. The regimes are selected in the same installation.
The checks follow NIST SP 800-53, the Kubernetes Pod Security Standards (Pod Security) and the Kubernetes hardening guidance of the United States National Security Agency and Cybersecurity and Infrastructure Security Agency (NSA and CISA). The Pod Security Standards are three built-in levels, privileged, baseline and restricted, of what a workload may do to the server it runs on, such as running as root or reading the server's own files. Kubernetes enforces the level set for each namespace.
Regimes
Across the GCC, and beyond it.
The regimes available today are from regulators in the Gulf Cooperation Council (GCC), in Singapore and in Iraq. The GCC's six member states are Saudi Arabia, the United Arab Emirates, Qatar, Kuwait, Bahrain and Oman.
Further regimes are added in a decided order, each becoming available once it is built and tested by Mamluk. A regime's scope may change until it is released.
| Country | Regime | Availability |
|---|---|---|
| Saudi Arabia | NCA Essential Cybersecurity Controls, ECC-2:2024 | Available |
| Saudi Arabia | SAMA Cyber Security Framework | Available |
| Qatar | Qatar Central Bank, Technology Risks | Available |
| Qatar | National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency | Available |
| United Arab Emirates | UAE Information Assurance Standard v2.1 | Available |
| United Arab Emirates | Central Bank of the UAE, Operational Risk Management Regulation, for banks | Available |
| Singapore | Monetary Authority of Singapore, Technology Risk Management | Available |
| Iraq | Central Bank of Iraq, Cyber Resilience Controls and Banking Reform Standards B2, B3, B7 and B9 | Available |
| Saudi Arabia | SAMA Cyber Resilience Fundamental Requirements, for new and sandbox financial entities | Coming soon |
| Bahrain | Central Bank of Bahrain Rulebook, module OM-5.5, for conventional and Islamic banks | Coming soon |
| Kuwait | Central Bank of Kuwait Cyber and Operational Resilience Framework | Coming soon |
Mamluk's work in each country is described on mamluk.net: Saudi Arabia, the United Arab Emirates, Qatar and the GCC.
How it fits
On Tersane, with BKE or on your own Kubernetes.
- Requires Bahriya Tersane. The convoy installs on the Tersane kyverno and trivy-operator charts, which every Tersane licence includes, or on your own installation of either at a supported version.
- With the Bahriya Kubernetes Engine. The convoy runs on BKE 2.2.0 and later, which provide Kubernetes 1.36. From BKE 2.3.0, BKE provides the hardening the platform requirements ask for, among them audit logging, encryption of Secrets at rest, Pod Security defaults, control-plane and kubelet settings, a trusted time source and a host firewall, and declares each one to the convoy, which reports it as provided by the platform. On BKE 2.2.0, as on another distribution, those requirements are reported for your evidence.
- On another distribution. The convoy runs on any conformant Kubernetes at version 1.36 or later. The platform requirements are then reported as not evidenced by the cluster, and the report asks for your evidence of them instead.
- Inside your perimeter. The report and its data stay in your cluster. The convoy's own NetworkPolicy permits no traffic out except to the email server or storage you configure, and nothing is sent to Mamluk. Every image the convoy uses is published in Mamluk's registry, signed, for you to mirror into your own.
What it is not
Evidence for your assessor, not a certificate.
The convoy maps a regime's technical controls to your cluster and records the evidence for them. The mapping is Mamluk's. It does not make an organisation compliant and does not certify compliance: the organisational requirements remain your organisation's to evidence, and compliance is determined by your assessor. The report says so on its first page.
An add-on
The Compliance App.
An add-on to the convoy, in which your organisation's people read the reports themselves. It runs in your own cluster, beside the convoy, and the reports never leave it. It is licensed at USD 12,000 per organisation, per year, whatever the number of regimes; the convoy's web view and email reports remain included without it.
- Sign-in. Through your organisation's own identity provider, or with local accounts where none is connected yet.
- Roles. For auditors, compliance leads, namespace owners and administrators, each seeing what the role allows; a namespace owner sees only their own namespaces.
- The evidence. Each regime's results over time, what to fix first, and downloads of the report, the OSCAL assessment results and the signed manifest.
Glossary
The organisations, standards and tools the convoy's pages name.
- NIST National Institute of Standards and Technology
- NIST is the United States government's standards agency. Its security publications are free to use, and regulators and auditors outside the United States also use them as a common reference.
- SP 800-53 NIST Special Publication 800-53, Revision 5
- SP 800-53 is a control catalogue: a numbered list of safeguards, each stating one thing an organisation should do, such as AC-6, least privilege, or AU-11, keeping audit records for a set period. Its controls are grouped in 20 families, and because the catalogue is detailed and open, it serves as a common language between regulations that are each written in their own terms.
- NCA National Cybersecurity Authority
- NCA is Saudi Arabia's national authority for cybersecurity. It sets the cybersecurity requirements for government entities and the operators of critical national infrastructure, and assesses compliance with them.
- ECC Essential Cybersecurity Controls
- The ECC are NCA's minimum cybersecurity requirements, binding on government entities and critical national infrastructure in Saudi Arabia. The current edition, ECC-2:2024, holds 176 requirements in four domains.
- SAMA Saudi Central Bank
- SAMA regulates banks, insurers, financing companies and other financial institutions in Saudi Arabia. It keeps the abbreviation of its former name, the Saudi Arabian Monetary Authority.
- SAMA CSF SAMA Cyber Security Framework
- The Cyber Security Framework sets the cybersecurity requirements for the organisations SAMA regulates, as control considerations in four domains. It is distinct from NIST's Cybersecurity Framework, which is also abbreviated CSF.
- QCB Qatar Central Bank
- QCB is Qatar's central bank and the regulator of its banks. Its circular on technology risks, issued in January 2018, sets the technology and cybersecurity requirements for the banks it regulates, in 516 numbered statements.
- NCSA National Cyber Security Agency
- The National Cyber Security Agency is Qatar's national authority for cybersecurity. Its national standards include the National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency.
- Qatar NIA National Information Assurance Standard
- The National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency in May 2023, applies to all organisations, which it defines as businesses operating within the State of Qatar, and to their information assets. It holds 356 control statements in 26 domains, and marks each as a baseline or an additional control.
- MAS Monetary Authority of Singapore
- The Monetary Authority of Singapore is Singapore's central bank and the regulator of its financial sector. It issues binding notices to banks, insurers and capital markets intermediaries, and guidelines that set out the good practice it expects them to adopt.
- MAS TRM MAS Technology Risk Management
- MAS's Notices FSM-N05, on technology risk management, and FSM-N06, on cyber hygiene, in force from 10 May 2024, and its Technology Risk Management Guidelines of January 2021. The notices are binding; the Guidelines are guidance, adopted in proportion to an institution's risks. The convoy holds them in one regime of 259 requirements and marks each as binding or guidance.
- CBI Central Bank of Iraq
- The Central Bank of Iraq licenses and regulates Iraq's banks and payment service providers. It issues the Cyber Resilience Controls for the financial and banking sector, and the Banking Reform Standards assessed for private banks.
- CBI regime CBI Cyber Resilience Controls and Banking Reform Standards
- The CBI's Cyber Resilience Controls (June 2024), published in Arabic, which apply to every bank and payment provider, and standards B2, B3, B7 and B9 of its Banking Reform Standards 2025, which apply to private banks. The convoy holds them in one regime of 524 requirements and marks each as Controls or Standards.
- CBUAE Central Bank of the UAE
- The CBUAE licenses and regulates banks and other financial institutions in the United Arab Emirates. Its Operational Risk Management Regulation sets their requirements for information and communications technology and cybersecurity, and requires them to comply with the cybersecurity regulations of the other UAE authorities.
- UAE CSC UAE Cyber Security Council
- The Cyber Security Council is the federal authority for cybersecurity in the United Arab Emirates, and issues the UAE Information Assurance Standard.
- UAE IA UAE Information Assurance Standard
- The Information Assurance Standard is the UAE's federal standard of security controls, binding on federal government entities and on critical information infrastructure, banks among them. Version 2.1 holds 134 controls in fifteen families, and maps each control to NIST SP 800-53 itself.
- GCC Gulf Cooperation Council
- The GCC's six member states are Saudi Arabia, the United Arab Emirates, Qatar, Kuwait, Bahrain and Oman.
- namespace
- A namespace is a named partition of a Kubernetes cluster, which usually holds one application's or one team's workloads. Permissions and policies are commonly set per namespace.
- admission policy
- An admission policy is a rule Kubernetes applies to each object as it is created or changed, before the object is stored. It can warn about the object and record the result, or refuse the object.
- Kyverno
- Kyverno is an open-source policy engine for Kubernetes. The convoy uses it for what Kubernetes cannot do by itself, such as verifying an image's signature, and reads the results of its own policies from Kyverno's policy reports.
- trivy-operator
- trivy-operator is an open-source security scanner that runs inside the cluster. It scans every workload's images for known vulnerabilities, and audits each workload's configuration and the permissions granted in the cluster.
- NetworkPolicy
- A NetworkPolicy is the Kubernetes object that states which network traffic may reach a group of workloads. A workload that no NetworkPolicy selects accepts traffic from anywhere in the cluster.
- Pod Security Kubernetes Pod Security Standards
- The Pod Security Standards are three built-in levels, privileged, baseline and restricted, of what a workload may do to the server it runs on, such as running as root or reading the server's own files. Kubernetes enforces the level set for each namespace.
- OSCAL Open Security Controls Assessment Language
- OSCAL is NIST's machine-readable format for control catalogues and assessment results. Governance, risk and compliance tools import results in it, so findings need not be typed in again.
- NSA and CISA National Security Agency and Cybersecurity and Infrastructure Security Agency
- The two United States agencies publish joint guidance on hardening Kubernetes, which the convoy's checks also follow.
Price and availability
The convoy is licensed separately from Tersane, at USD 24,000 per regulatory regime, per organisation, per year, with the Tersane core licence; there is no base fee. The Compliance App is an add-on at USD 12,000 per organisation, per year. NCA ECC, SAMA CSF, QCB, Qatar NIA, UAE IA, CBUAE, MAS TRM and CBI are available; the convoy's installation and configuration are described in the documentation, and Activating a regime describes how a regime is added to the licence and to a running installation.
Discuss the convoy
To discuss the regimes your organisation must meet, or the convoy's licensing, contact Mamluk.
Contact Mamluk