Convoys · Compliance and Assurance · QCB
Qatar Central Bank: technology risks for banks.
Qatar. Regulator: Qatar Central Bank (QCB).
The convoy's regime for banks in Qatar. It holds every numbered statement of the Qatar Central Bank's Technology Risks circular of January 2018 under QCB's own numbers, enforces and checks those a Kubernetes cluster can show, and lists the rest as the bank's own evidence, in a dated report every day.
The screenshots on this page are taken on a test cluster with sample workloads.
Neither Mamluk LLC-FZ nor its products are affiliated with or endorsed by Qatar Central Bank.
In brief
Who sets these requirements, and how the convoy evidences them.
Qatar Central Bank (QCB). QCB is Qatar's central bank and the regulator of its banks. Its circular on technology risks, issued in January 2018, sets the technology and cybersecurity requirements for the banks it regulates, in 516 numbered statements.
The convoy classes each requirement by how its evidence is obtained: enforced by an admission policy, checked in the cluster, provided by the platform, or the organisation's own evidence. An admission policy is a rule Kubernetes applies to each object as it is created or changed, before the object is stored. It can warn about the object and record the result, or refuse the object. How a regulator's requirement becomes evidence follows one requirement from the regulator's text to the result in the report.
Who it applies to
Banks regulated by the Qatar Central Bank.
The Qatar Central Bank's technology risk circular, issued in January 2018, binds the banks it regulates in Qatar, and each bank reports its compliance to QCB every year. QCB regulates payment service providers, financial services operators and insurers under instruments of their own, which this regime does not cover.
The circular favours infrastructure under the bank's own control: it treats a private facility the bank controls as the alternative to keeping critical data in a cloud it does not. A cluster on the bank's premises, with the convoy's evidence kept inside it, is that arrangement.
Structure
Ten sections, 516 numbered statements.
The circular is arranged by the part of the bank responsible, from governance and the departments that support it to IT operations, the security of the enterprise's infrastructure and data, and its business applications. Its statements are numbered to four levels. The convoy maps each numbered statement, the smallest unit QCB numbers, so the report gives a result for each one, under QCB's own number. The descriptions below are Mamluk's; the circular's text is not reproduced.
- 1 Cyber security governance and its organisation 21
- 2 People: personnel security and staff competence 20
- 3 Legal and compliance 15
- 4 Procurement 6
- 5 Risk management 16
- 6 Business continuity and recovery 16
- 7 Reporting compliance to QCB 4
- 8 IT operations 138
- 9 Infrastructure, network and data security 209
- 10 Business applications 71
Evidence
516 statements, each with exactly one result.
The convoy holds all 516 numbered statements of the circular, across its ten sections, under QCB's own numbers, with a short description of what each asks written by Mamluk; QCB's text is not reproduced, and the authoritative wording remains QCB's circular. Each statement is classed by how its evidence is obtained:
| Section | Enforced | Checked | Platform | The bank's evidence | Total |
|---|---|---|---|---|---|
| 1 Governance | 0 | 0 | 0 | 21 | 21 |
| 2 People | 0 | 1 | 0 | 19 | 20 |
| 3 Legal and compliance | 0 | 0 | 0 | 15 | 15 |
| 4 Procurement | 0 | 0 | 0 | 6 | 6 |
| 5 Risk management | 0 | 2 | 0 | 14 | 16 |
| 6 Business continuity | 0 | 0 | 0 | 16 | 16 |
| 7 Reporting compliance to QCB | 0 | 0 | 0 | 4 | 4 |
| 8 IT operations | 1 | 15 | 12 | 110 | 138 |
| 9 Infrastructure, network and data security | 5 | 8 | 14 | 182 | 209 |
| 10 Business applications | 0 | 2 | 1 | 68 | 71 |
| All statements | 6 | 28 | 27 | 455 | 516 |
- Enforced (6). An admission policy of the convoy flags, and once you choose blocks, what the statement asks for: network access restricted to authorised services (8.10.1.9), segmentation in the network design (9.1.1.3), unneeded connections to critical networks closed (9.1.1.7), classification labels for information and applications (9.2.1.5, 9.7.1.3), and restricted outbound connections (9.7.2.1). The report shows the policy's result for every object it applies to.
- Checked (28). The convoy observes the statement in the cluster and reports it: least privilege and role-based access (2.1.9, 8.10.1.2), privileged accounts and access review (8.4.8, 8.10.1.6, 8.10.4.2, 8.10.4.4), the inventories (5.1.4, 5.1.5, 8.8.2, 8.8.5, 9.1.1.2), patching and the platform's versions (8.3.2, 8.3.3, 8.3.6, 8.8.4, 9.1.14.7), the separation of production from staging, test and development (8.1.7, 9.7.1.2), hardening (9.1.1.8), backups kept off site and encrypted (8.7.2, 8.7.3), logs sent to a central store (8.4.10), and vulnerability assessment (9.1.1.5, 9.4.2.2, 9.4.2.3, 9.4.3.1, 10.10.8, 10.15.3). Image scanning is one part of what QCB asks for vulnerability assessment; penetration testing remains the bank's.
- Platform (27). The platform provides the control and the convoy reports it: unique identity and authentication for access to the cluster, with sign-in delegated to the bank's identity provider, which is the bank's to evidence for multi-factor authentication (8.10.2, 8.10.5.2), Kubernetes' default identities disabled: anonymous access refused and no default service account token in Pods (9.1.1.6), audit logging of every account, privileged ones included, kept for the six months 8.4.7 requires (8.1.11, 8.4.4, 8.4.7, 8.10.4.1, 9.1.1.4, 9.1.1.9), encryption in transit and at rest and the keys that protect it (9.1.1.12, 9.2.2.2, 9.6.1), and a trusted time source (9.1.9.3). BKE declares these facts from 2.3.0; on earlier BKE versions and on other distributions, these statements are reported as not evidenced by the cluster, and the report asks for the bank's evidence of them.
- The bank's evidence (455). Governance, people, legal and compliance, procurement, risk, business continuity and the annual report to QCB are the bank's to evidence, with most of IT operations, infrastructure security and business applications. The report lists each one as organisational evidence, technical or non-technical, so the record of the circular is complete and nothing is presented as covered that is not.
All 61 technical statements are partly technical: the cluster evidences its own part, and the report also asks for the bank's evidence of the rest. Where the limit is not plain from the statement, the report states the scope of the evidence beneath it: for 9.1.1.3, for example, the cluster evidences network segmentation only, and the other measures of a defence-in-depth design are the bank's. Where the circular sets a figure, the convoy uses QCB's value: event logs kept for at least six months, rather than the twelve that Saudi Arabia's Essential Cybersecurity Controls (NCA ECC) require.
The report
In QCB's numbering, from the cluster itself.
Each run writes the report in HTML and PDF, with OSCAL assessment results and a signed manifest, to a volume in your cluster, and delivers it to the email addresses and storage you configure. Each image opens at full size when selected.
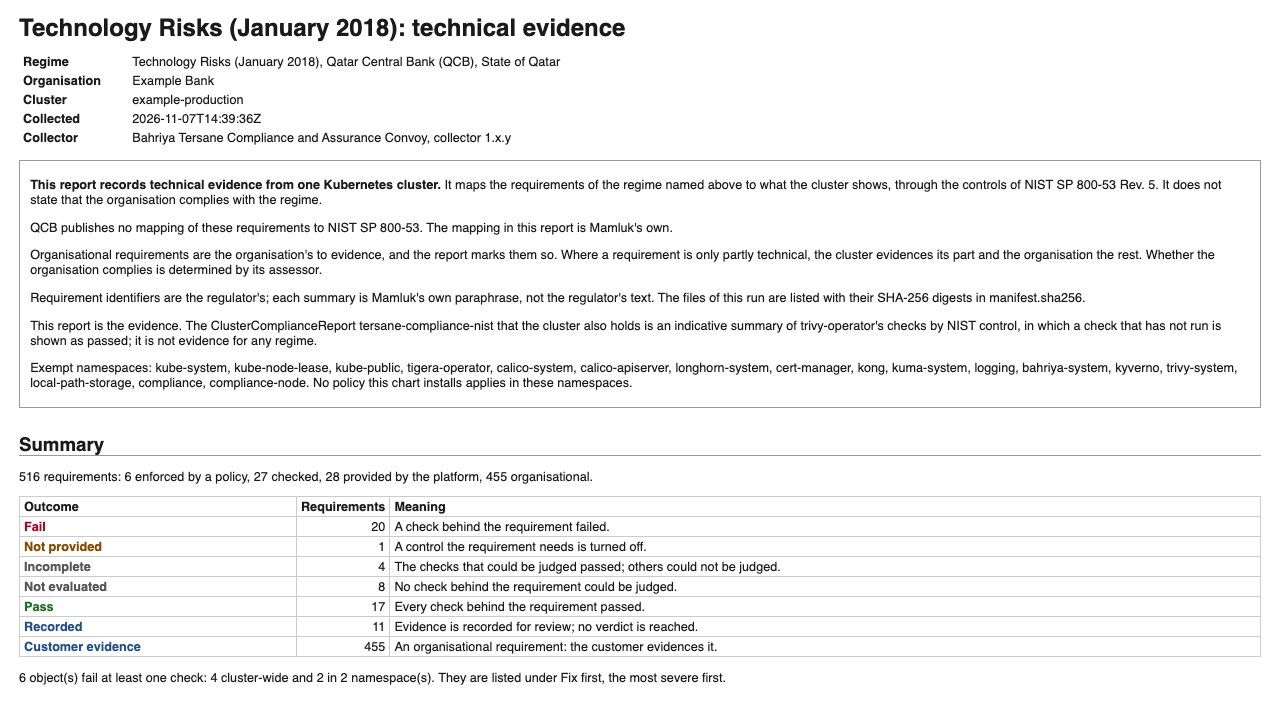
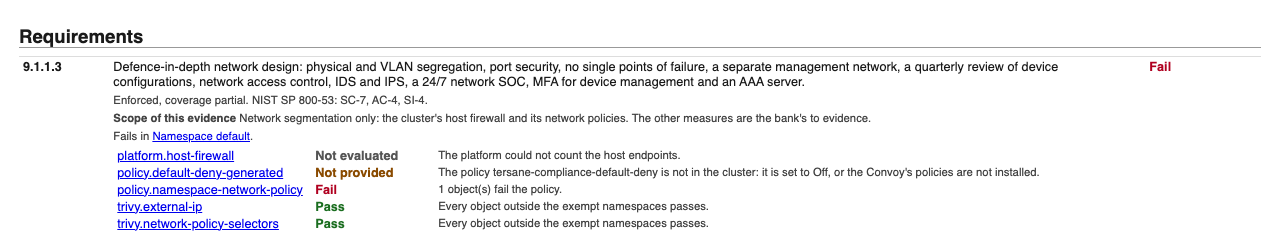
Sample report
A sample, written by the convoy on a test cluster with sample workloads, for the organisation "Example Bank". Its image versions and cluster name are placeholders, and its run date and regime version are those of the sample, not of a release.
Corrections
Corrections to earlier reports.
A review of every statement's class (Compliance 0.16.0). Each statement was read again against the checks its NIST controls reach. These outcomes change from earlier reports; every other outcome is as before.
- 9.1.13.2 to 9.1.13.5 concern virtual machines, hypervisors and their management. Earlier reports judged them by the cluster's own hardening, access control, patching and audit log, which say nothing of the virtualisation layer beneath it. They are now the bank's to evidence. The cluster's own results remain under 9.1.1.8, 8.10.1.2, 8.3.2 and 8.4.4.
- 9.1.1.6 (default accounts disabled) now has a verdict: whether anonymous requests are refused and whether Pods receive the default service account's token.
- 8.10.4.2 now takes its verdict on "logged" from the API server's audit log; earlier reports recorded it only.
- 8.7.2, 8.7.3 and 8.4.10 are now judged by new checks: an available Longhorn backup target with a recurring backup job, encrypted backed-up volumes, and Fluent Bit forwarding the cluster's logs to a central store.
If an assessor has read an earlier report, its results for 9.1.13.2 to 9.1.13.5 should be read as evidence about the cluster, not about the virtualisation layer, which remains the bank's to evidence.
8.3.6, 8.4.8, 8.8.4, 8.10.1.6, 8.10.4.4 and 9.1.1.5. Reports made before this correction showed 8.4.8, 8.8.4, 8.10.1.6, 8.10.4.4 and 9.1.1.5 as Pass in error, and judged 8.3.6 by whether any vulnerability was open. Each now shows Recorded.
- 8.4.8 asks for a six-monthly review of user access, 8.10.1.6 for a periodic audit of accounts against current roles, and 8.10.4.4 for a current list of privileged users. The report records the cluster's role bindings for each, but no rule can judge from them whether the review took place. The Pass came from a different check: that people sign in through an identity provider. That is true, but it does not evidence a review.
- 8.3.6 asks for the delay in patching to be measured against the bank's baseline. The report now records the age of each open vulnerability, and no longer gives a verdict from whether any vulnerability is open.
- 8.8.4 asks for end-of-life and end-of-support dates to be tracked. The Pass came from the scans of the workloads' images, which judge whether critical or high vulnerabilities are open, not whether an image's operating system is still supported. The report now records the versions of the Bahriya Kubernetes Engine and Kubernetes that the cluster runs, and no check judges support.
- 9.1.1.5 asks for infrastructure and network devices to be tested for vulnerabilities. The Pass came from the scans of the workloads' images, which do not reach the control plane, the platform or network devices. The report now records the versions of the Bahriya Kubernetes Engine and Kubernetes that the cluster runs, and its inventory.
If an assessor has read an earlier report, its Pass for 8.4.8, 8.10.1.6 and 8.10.4.4 should be read as evidence that people sign in through the organisation's identity provider, and its Pass for 8.8.4 and 9.1.1.5 as evidence that the workloads' images carry no open critical or high vulnerability, and nothing more. The review, the testing and the tracking of support dates remain the bank's to evidence.
At the same time, the two requirements on multi-factor authentication, 8.10.2.7 and 8.10.5.2, gained a scope. It states that the evidence is the delegation of sign-in to the identity provider, and that whether that provider requires a second factor is the organisation's to evidence. Six requirements whose verdict comes from the workloads but which name systems, devices, databases or assets beyond them (5.1.4, 8.3.2, 8.8.4, 9.1.13.4, 9.1.14.7 and 9.4.2.3) gained a scope saying what the verdict covers. Four requirements on identification and remote access (8.10.2.1, 8.10.2.2, 8.10.5.3 and 9.10.1.9) gained a scope saying that the verdict concerns sign-in through the identity provider, and that shared credentials such as kubeadm's admin.conf, and SSH access to the nodes, are the bank's to evidence. Their outcomes are unchanged.
The mapping
Mamluk's mapping, keyed to NIST.
Each requirement is mapped to the controls of NIST Special Publication 800-53, Revision 5 (SP 800-53), published by the National Institute of Standards and Technology (NIST), and each NIST control to the checks that evidence it in the cluster. NIST is the United States government's standards agency. Its security publications are free to use, and regulators and auditors outside the United States also use them as a common reference. SP 800-53 is a control catalogue: a numbered list of safeguards, each stating one thing an organisation should do, such as AC-6, least privilege, or AU-11, keeping audit records for a set period. Its controls are grouped in 20 families, and because the catalogue is detailed and open, it serves as a common language between regulations that are each written in their own terms.
The checks and their NIST mapping are shared by every regime. For each regime selected, the convoy collects evidence every day from the same cluster and the same scanner and policy reports, and reports it in its regulator's own numbering.
The circular states that it draws on Qatar's National Information Assurance Policy, the NIST Cybersecurity Framework and ISO/IEC 27001, but it maps none of its statements to them.
The regulator publishes no official crosswalk to NIST, so the mapping is Mamluk's own. Before the regime was released, it was checked against the regulator's text a second time, statement by statement, by a reviewer other than its author.
The report states whose mapping it uses, in these words: “QCB publishes no mapping of these requirements to NIST SP 800-53. The mapping in this report is Mamluk's own.” It records the technical evidence the cluster provides; it does not make an organisation compliant, and compliance is determined by your assessor.
Regimes
One convoy, every regime.
Every regime runs in the same installation of the convoy. An organisation that answers to two regulators selects both, and each is licensed separately.
Glossary
The organisations, standards and tools the convoy's pages name.
- NIST National Institute of Standards and Technology
- NIST is the United States government's standards agency. Its security publications are free to use, and regulators and auditors outside the United States also use them as a common reference.
- SP 800-53 NIST Special Publication 800-53, Revision 5
- SP 800-53 is a control catalogue: a numbered list of safeguards, each stating one thing an organisation should do, such as AC-6, least privilege, or AU-11, keeping audit records for a set period. Its controls are grouped in 20 families, and because the catalogue is detailed and open, it serves as a common language between regulations that are each written in their own terms.
- NCA National Cybersecurity Authority
- NCA is Saudi Arabia's national authority for cybersecurity. It sets the cybersecurity requirements for government entities and the operators of critical national infrastructure, and assesses compliance with them.
- ECC Essential Cybersecurity Controls
- The ECC are NCA's minimum cybersecurity requirements, binding on government entities and critical national infrastructure in Saudi Arabia. The current edition, ECC-2:2024, holds 176 requirements in four domains.
- SAMA Saudi Central Bank
- SAMA regulates banks, insurers, financing companies and other financial institutions in Saudi Arabia. It keeps the abbreviation of its former name, the Saudi Arabian Monetary Authority.
- SAMA CSF SAMA Cyber Security Framework
- The Cyber Security Framework sets the cybersecurity requirements for the organisations SAMA regulates, as control considerations in four domains. It is distinct from NIST's Cybersecurity Framework, which is also abbreviated CSF.
- QCB Qatar Central Bank
- QCB is Qatar's central bank and the regulator of its banks. Its circular on technology risks, issued in January 2018, sets the technology and cybersecurity requirements for the banks it regulates, in 516 numbered statements.
- NCSA National Cyber Security Agency
- The National Cyber Security Agency is Qatar's national authority for cybersecurity. Its national standards include the National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency.
- Qatar NIA National Information Assurance Standard
- The National Information Assurance Standard, version 2.1, issued by the National Cyber Security Agency in May 2023, applies to all organisations, which it defines as businesses operating within the State of Qatar, and to their information assets. It holds 356 control statements in 26 domains, and marks each as a baseline or an additional control.
- MAS Monetary Authority of Singapore
- The Monetary Authority of Singapore is Singapore's central bank and the regulator of its financial sector. It issues binding notices to banks, insurers and capital markets intermediaries, and guidelines that set out the good practice it expects them to adopt.
- MAS TRM MAS Technology Risk Management
- MAS's Notices FSM-N05, on technology risk management, and FSM-N06, on cyber hygiene, in force from 10 May 2024, and its Technology Risk Management Guidelines of January 2021. The notices are binding; the Guidelines are guidance, adopted in proportion to an institution's risks. The convoy holds them in one regime of 259 requirements and marks each as binding or guidance.
- CBI Central Bank of Iraq
- The Central Bank of Iraq licenses and regulates Iraq's banks and payment service providers. It issues the Cyber Resilience Controls for the financial and banking sector, and the Banking Reform Standards assessed for private banks.
- CBI regime CBI Cyber Resilience Controls and Banking Reform Standards
- The CBI's Cyber Resilience Controls (June 2024), published in Arabic, which apply to every bank and payment provider, and standards B2, B3, B7 and B9 of its Banking Reform Standards 2025, which apply to private banks. The convoy holds them in one regime of 524 requirements and marks each as Controls or Standards.
- CBUAE Central Bank of the UAE
- The CBUAE licenses and regulates banks and other financial institutions in the United Arab Emirates. Its Operational Risk Management Regulation sets their requirements for information and communications technology and cybersecurity, and requires them to comply with the cybersecurity regulations of the other UAE authorities.
- UAE CSC UAE Cyber Security Council
- The Cyber Security Council is the federal authority for cybersecurity in the United Arab Emirates, and issues the UAE Information Assurance Standard.
- UAE IA UAE Information Assurance Standard
- The Information Assurance Standard is the UAE's federal standard of security controls, binding on federal government entities and on critical information infrastructure, banks among them. Version 2.1 holds 134 controls in fifteen families, and maps each control to NIST SP 800-53 itself.
- GCC Gulf Cooperation Council
- The GCC's six member states are Saudi Arabia, the United Arab Emirates, Qatar, Kuwait, Bahrain and Oman.
- namespace
- A namespace is a named partition of a Kubernetes cluster, which usually holds one application's or one team's workloads. Permissions and policies are commonly set per namespace.
- admission policy
- An admission policy is a rule Kubernetes applies to each object as it is created or changed, before the object is stored. It can warn about the object and record the result, or refuse the object.
- Kyverno
- Kyverno is an open-source policy engine for Kubernetes. The convoy uses it for what Kubernetes cannot do by itself, such as verifying an image's signature, and reads the results of its own policies from Kyverno's policy reports.
- trivy-operator
- trivy-operator is an open-source security scanner that runs inside the cluster. It scans every workload's images for known vulnerabilities, and audits each workload's configuration and the permissions granted in the cluster.
- NetworkPolicy
- A NetworkPolicy is the Kubernetes object that states which network traffic may reach a group of workloads. A workload that no NetworkPolicy selects accepts traffic from anywhere in the cluster.
- Pod Security Kubernetes Pod Security Standards
- The Pod Security Standards are three built-in levels, privileged, baseline and restricted, of what a workload may do to the server it runs on, such as running as root or reading the server's own files. Kubernetes enforces the level set for each namespace.
- OSCAL Open Security Controls Assessment Language
- OSCAL is NIST's machine-readable format for control catalogues and assessment results. Governance, risk and compliance tools import results in it, so findings need not be typed in again.
- NSA and CISA National Security Agency and Cybersecurity and Infrastructure Security Agency
- The two United States agencies publish joint guidance on hardening Kubernetes, which the convoy's checks also follow.
Price and availability
Each regime is licensed at USD 24,000 per organisation, per year, with the Tersane core licence; there is no base fee. The convoy needs a version of Kubernetes which BKE provides; the prerequisites give the requirement. See the Compliance and Assurance Convoy for how it works, and its documentation for installation. Activating a regime describes how a regime is added to the licence and to a running installation. Its reports can be read in your own cluster, by role, in the Compliance App.
Discuss QCB
To discuss the regimes your organisation must meet, or the convoy's licensing, contact Mamluk.
Contact Mamluk